Rethink Networking: Identity-drive, Zero-Trust by Design
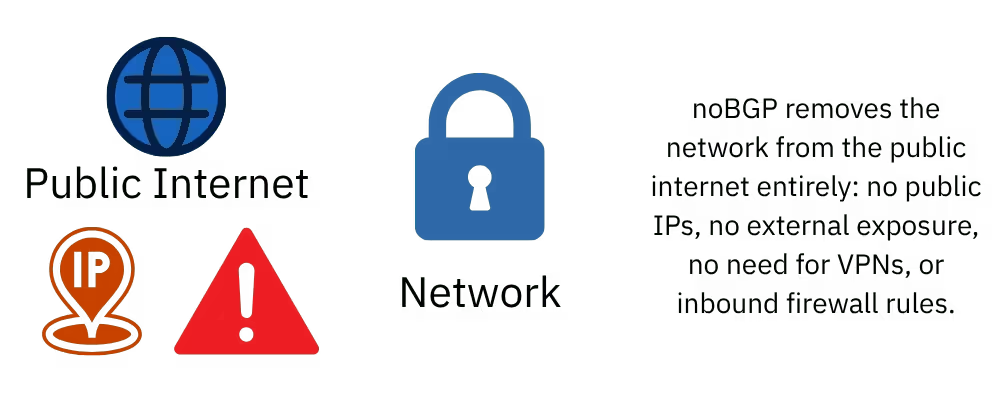
noBGP replaces traditional IP-based networking with an intent-based overlay network prioritizing identity, policy, and deterministic routing. A radically simpler, inherently secure foundation for zero-trust networking; without the need for public IPs, VPNs, or perimeter defense layers.
1. Keep Private Resources Off the Public Internet
With noBGP, resources never need public IP addresses to be reachable. You make connections based on identity and policy, not IP and port exposure. This means:
- No public endpoints to scan or attack
- No need for external firewalls or WAFs
- Reduced EASM complexity
Your infrastructure effectively disappears from the public internet.
2. Control Data Routes with Precision
Zero trust isn’t only about access; also about where your data flows. With noBGP, you get to:
- Enforce routing policies avoiding untrusted ISPs, regions, or cloud providers
- Define routes based on trust, latency, cost, or compliance
- Create deterministic, auditable data paths
Unlike BGP, which relies on third-party AS paths, noBGP gives you control over the journey.
3. Grant (and Revoke) Temporary Access
Zero trust means access is enough and in time. With noBGP:
- You scope access to sessions, users, workloads, or automation
- Ideal for burst workloads like CI/CD pipelines or AI training jobs
- You revoke access instantly without requiring firewall or VPN updates
This makes supporting ephemeral infrastructure or contractors easy without lingering risk.
4. Eliminate Legacy Security Bloat
By making the network private by default, noBGP reduces or eliminates the need for:
- VPNs and their configuration headaches
- Public IP firewall rules
- EASM tools trying to monitor exposure you cannot control
Fewer tools, fewer rules, and less human error.
Getting Started with Zero-Trust Networking Using noBGP
Here’s how to begin implementing zero trust with noBGP in your environment:
Step 1:
Identify Resources
Determine which services or devices you should protect under a zero-trust model. This might include:
- Internal APIs and microservices
- Admin dashboards and tools
- Development environments or lab systems
- Remote or on-prem devices
Step 2:
Deploy noBGP
Set up noBGP agents on your workloads or gateways. Agents establish outbound-only, encrypted, identity-based connections across clouds or sites.
No inbound ports. No public IPs. No NAT traversal required.
Step 3:
Define Routing Policies
Use networking policies to describe how data is routed:
- "Keep data in the EU"
- "Only use preferred ISPs and Cloud Providers for routes"
You can define and enforce these policies simply, and they scale without configuration sprawl.
Step 4:
Monitor & Evolve
Use built-in logs and access visibility to:
- Audit connection behavior
- Revoke unused access
- Adapt policies as your architecture evolves
noBGP integrates well with identity providers and logging tools, making this step straightforward.
Zero Trust, Made Real
Implementing zero-trust networking doesn’t have to be overwhelming. With noBGP, you:
✅ Remove public exposure
✅ Control where data flows
✅ Automate and revoke access
✅ Eliminate legacy security debt
As more organizations adopt microservices, hybrid cloud, and dynamic infrastructure, zero-trust networking becomes the standard. noBGP makes this practical, efficient, and cloud-native from day one.
