Packet Switching: The Backbone of Modern Data Networks
Introduction
Every email, video stream, or cloud API request you send travels not as a continuous stream, but as a collection of discrete chunks called packets. This method, known as packet switching, is the foundation of modern networking and the internet.
Understanding how packet switching works helps you grasp key network behaviors like latency, jitter, congestion, and the need for higher-layer protocols like TCP. In this article, we’ll explain what packet switching is, how it’s different from circuit switching, and how noBGP brings predictability and control to an otherwise dynamic system.
What is Packet Switching?
Packet switching is a method of data transmission where information is broken into small packets and sent independently across the network. Each packet may take a different path to reach the destination, where they’re reassembled into the original message.
Core Concepts:
- Data is split into packets
- Each packet has a header (routing info) and payload (data)
- Routers make independent forwarding decisions per packet
- Packet order and timing are not guaranteed
How Packet Switching Works
- Your device breaks data (e.g., a video stream) into packets.
- Each packet is labeled with:
- Source and destination IP
- Sequence number
- Protocol type (TCP, UDP)
- Packets are routed through the network individually.
- At the destination, packets are reassembled into the original message.
Diagram: Packet Switching Flow
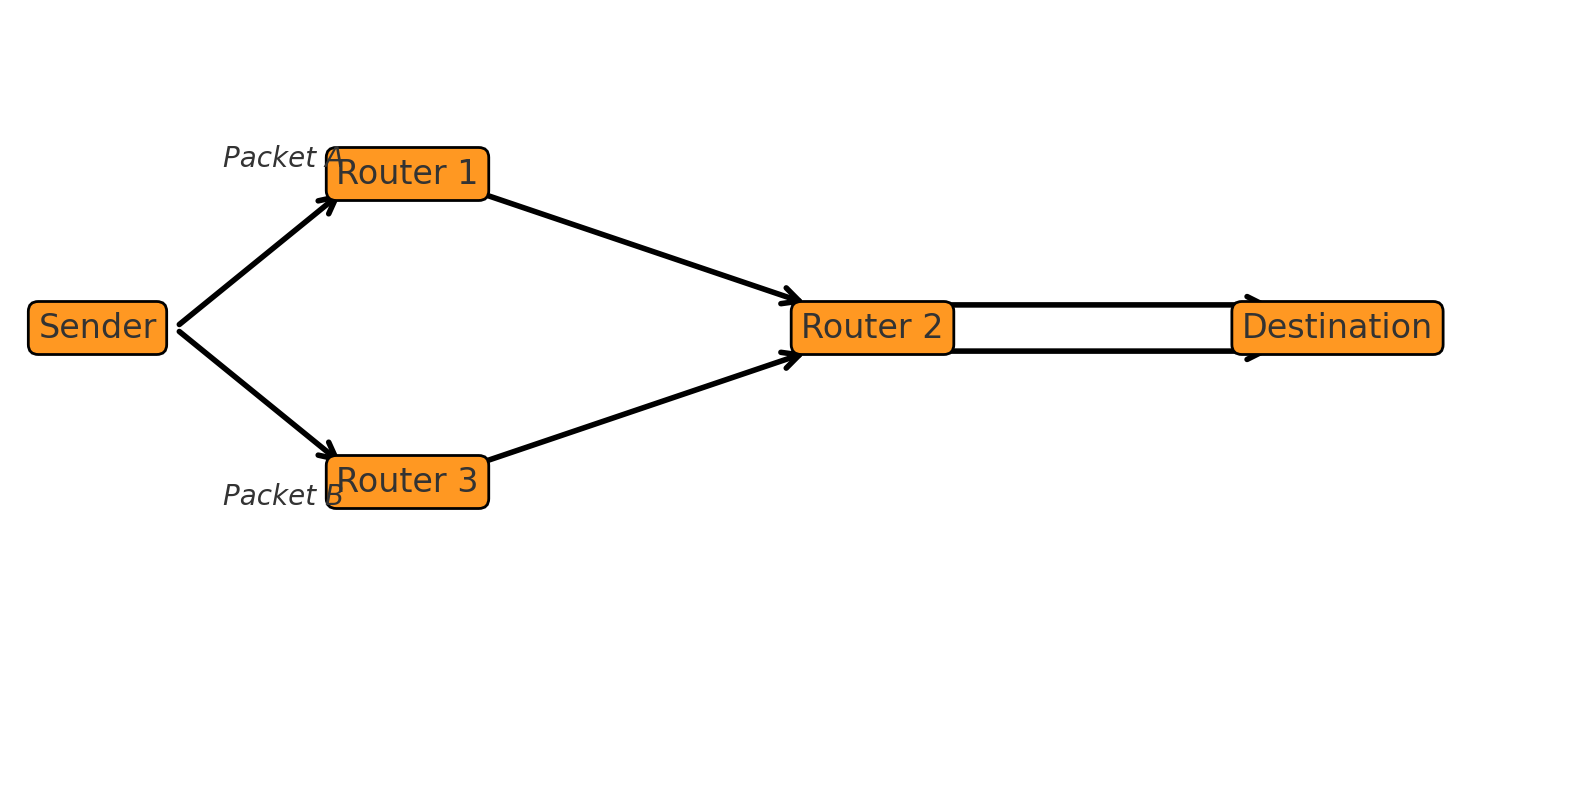
Unlike circuit switching, there’s no fixed path. Each router decides the next hop dynamically.
Advantages of Packet Switching
Benefit
Description
Efficiency
Network resources are shared across connections
Scalability
Supports millions of devices and routes
Resilience
Packets reroute if paths fail
Cost-effective
No idle reserved channels needed
Disadvantages of Packet Switching
Drawback
Description
Variable delay
Packets can arrive at different times
Packet loss
Network congestion can cause drops
Reassembly required
Requires higher-layer protocols like TCP
Less control
You don't control the path traffic takes
Packet Switching vs Circuit Switching
Feature
Packet Switching
Circuit Switching
Path type
Dynamic, per packet
Fixed, per session
Efficiency
High
Low (idle time waste)
Latency
Variable
Consistent
Use case
Data (web, video, etc.)
Voice (legacy PSTN)
Modern networks
✅ Dominant
❌ Obsolete for data
Where Packet Switching is Used
Today, packet switching is used everywhere:
- The Internet: Core backbone and edge networks
- Cloud platforms: AWS, Azure, and GCP VPCs
- Mobile networks: LTE and 5G for app data
- Voice over IP (VoIP): Voice encoded in IP packets
- Streaming and gaming: Real-time media and input handling
Protocols that use packet switching include:
Protocol
Layer
Use Case
IP
3
Routing packets across networks
TCP
4
Reliable delivery
UDP
4
Low-latency media or gaming
HTTP/HTTPS
7
Web and API traffic
Why Packet Switching Needs Control
While packet switching is flexible, it introduces uncertainty:
- Route unpredictability: You don’t know where your packets are going
- Security risks: Packets pass through third-party routers
- Performance issues: Packets may take congested or long paths
- Troubleshooting complexity: Dynamic routing is hard to debug
Protocols like BGP attempt to manage the chaos—but offer no guarantees.
How noBGP Reinvents Packet-Based Networking
Packet switching isn’t the problem—lack of control is.
noBGP brings deterministic control and policy-based decision-making to packet-switched networks. You still get the efficiency and scalability of packet switching, but without the unpredictability.
Key Benefits of noBGP in a Packet-Switched World:
- Deterministic Routing
- Choose how your packets travel—based on latency, region, or policy.
- Identity-Based Connections
- Route between workloads without relying on IP or subnet constraints.
- End-to-End Encryption
- Every packet is encrypted. No exposure to BGP hijacks or man-in-the-middle attacks.
- Cross-Cloud and VPC Connectivity
- No NAT, no IP overlaps, no VPNs. Just clean, private routing.
- Real-Time Rerouting
- Packets take the best available route—not the one BGP guessed hours ago.
Summary: Packet Switching vs noBGP’s Approach
Feature
Traditional Packet Switching
noBGP Layer on Top
Routing Decisions
Per-hop, dynamic
Deterministic, policy-driven
Visibility
Low
Full path awareness
Subnet/IP dependency
High
None
Encryption
Optional
Built-in
Troubleshooting
Difficult
Transparent, auditable
Multi-cloud connectivity
Complex with VPNs/BGP
Seamless with identity-based routing
Final Thoughts
Packet switching made the internet what it is. But while it brought efficiency, it also sacrificed predictability, privacy, and control. BGP and IP routing were layered on top—but they were designed in a different era.
noBGP upgrades packet-switched networking with the modern principles it’s been missing: clarity, determinism, and programmable intent.
You still get packets. You just finally get to decide where they go.
Choose your path. Choose noBGP.
