VPNs have been the go-to solution for securing network access for over two decades. Whether you’re connecting remote workers, cloud workloads, or data centers, chances are a VPN is involved. But VPNs were built for a different era, and their limitations show in today’s dynamic, distributed environments.
noBGP offers a modern alternative to VPNs by eliminating the complexity, exposure, and rigidity of legacy network connections. The platform enables private, secure, and policy-driven connectivity without relying on IP-based tunnels.
This article compares traditional VPNs vs. noBGP and shows why developers, IT teams, and security architects choose noBGP for secure workload-to-workload communication.
What Is a VPN?
A Virtual Private Network (VPN) creates an encrypted tunnel between two points over the public internet. Organizations commonly use VPNs to:
- Allow remote workers to access corporate resources
- Bridge different sites or cloud networks
- Hide internet traffic from outside observers
While VPNs provide encryption and access control, they come with drawbacks, especially at scale.
VPN Drawbacks in Modern Environments
❌ Public IP Exposure
Even though VPNs encrypt traffic, the endpoints themselves must have public IPs or open firewall ports. This increases your attack surface.
❌ Complex Setup & Maintenance
Setting up VPNs requires:
- IP address coordination
- NAT traversal
- Port forwarding
- Certificate or key management
And when something breaks? Debugging is painful and non-obvious.
❌ Scalability Challenges
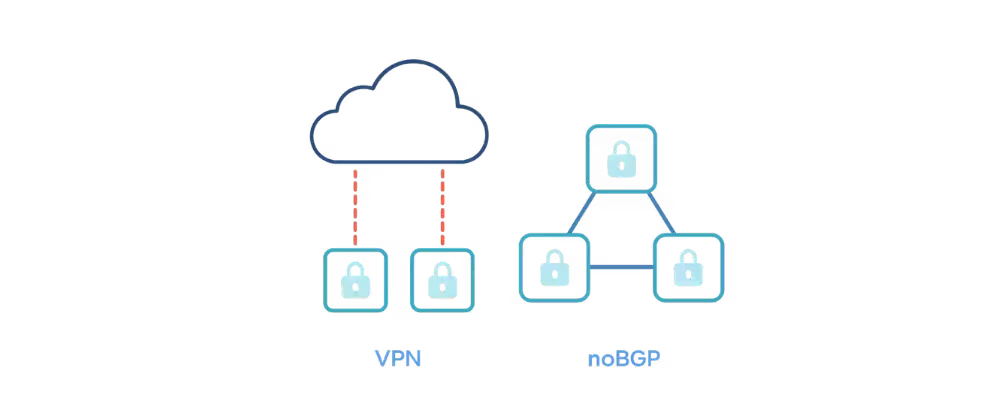
VPNs don’t scale easily. Connecting multiple regions, tenants, or clouds often leads to:
- Full mesh nightmares
- Overlapping CIDR conflicts
- Manual routing tables
How noBGP Solves These Problems
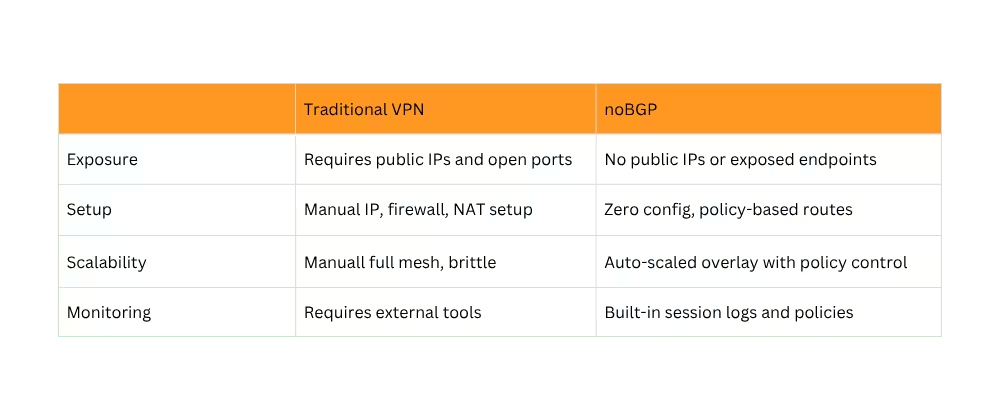
noBGP provides a modern networking architecture that delivers identity-based, encrypted, and deterministic communication between workloads anywhere.
Here’s how noBGP compares to VPNs:
Why noBGP Is a Better VPN Alternative
- No Public Exposure
With noBGP, your workloads don’t need public IPs to be reachable. All connections initiate outbound using secure identities. There’s:
- No scanning
- No open ports
- No attack surface
2. Frictionless Configuration
You don’t need to manage IP routes, CIDR overlaps, or NAT gateways. Define what service should talk to what; no network engineering required.
3. Cross-Cloud and On-Prem Ready
Traditional VPNs struggle with multi-cloud and hybrid environments. noBGP thrives in them, offering seamless overlay connectivity across:
- AWS, Azure, GCP
- Private data centers
- Edge devices
- Developer laptops
4. No Subnet Collisions
Overlapping CIDR blocks? No problem. Since noBGP uses identities, not IPs, you connect any workload without re-IPing or building custom NAT rules.
When Should You Replace a VPN with noBGP?
If you’re experiencing any of the following, the time has come to consider a shift:
✅ Your VPN setup grows in complexity
✅ You’re expanding across clouds or regions
✅ You’re tired of managing IPs, ports, and firewall rules
✅ You need temporary, scoped access (e.g. CI/CD, contractors)
Conclusion: VPNs Had Their Time; noBGP Is Built for Now
Engineers built traditional VPNs when networks were static and users worked in offices. That’s no longer the world we live in.
noBGP offers:
- Private-by-default architecture
- Policy-driven access
- Cross-cloud connectivity
- Simpler ops and better security
This isn’t a VPN replacement; this is a rethink of networking itself.
