VPN Protocols: A Guide to Secure Remote Access Technologies
Introduction
Virtual Private Networks (VPNs) allow users and devices to connect securely over public networks. Whether you’re a remote worker, cloud administrator, or IT security engineer, VPNs are a cornerstone of secure communication.
But not all VPNs are created equal. The underlying VPN protocol determines performance, encryption, compatibility, and ease of use.
In this guide, we’ll compare the most widely used VPN protocols—OpenVPN, IPSec, WireGuard, L2TP, SSTP, and IKEv2—and explore their strengths and limitations. We’ll also discuss how noBGP provides a next-generation alternative that avoids the complexity and limitations of traditional VPN protocols.
What Is a VPN Protocol?
A VPN protocol defines the method by which your data is encrypted, authenticated, and tunneled between your device and the remote endpoint.
Key Responsibilities:
- Establishing the tunnel
- Encrypting and decrypting traffic
- Handling reconnections and performance
- Ensuring authentication and data integrity
Popular VPN Protocols Explained
Protocol
Type
Encryption
Notes
OpenVPN
SSL/TLS-based
AES, ChaCha20
Open-source, flexible, widely used
IPSec
IP-level
AES, 3DES
Used in site-to-site and IKEv2 setups
Wireguard
Modern kernel-based
ChaCha20
Fast, lightweight, simpler config
L2TP/IPSec
Layer 2 + IPSec
AES
Legacy Windows compatibility
IKEv2/IPSec
Tunnel-based
AES
Mobile-friendly, reconnects well
SSTP
SSL-based
AES
Microsoft-specific, works with firewalls
VPN Protocol Comparison Table
Feature
OpenVPN
IPSec
WireGuard
IKEv2
SSTP
Speed
Medium
Medium
Fast
Fast
Medium
Encryption Strength
Strong
Strong
Strong
Strong
Strong
NAT Travesal
Yes
Limited
Yes
Yes
Yes
Mobile Compatibility
Good
Fair
Fair
Great
Good
Firewall Friendly
Yes
No
Yes
Yes
Yes
Config Complexity
High
High
Low
Medium
Low
Open Source
Yes
Yes
Yes
Partial
No
Use Cases for Different VPN Protocols
Scenario
Recommended Protocol
Remote workforce
OpenVPN, IKEv2
Connecting cloud VPCs
IPSec, WireGuard
Mobile device VPN
IKEv2/IPSec
Low-latency gaming or VoIP
WireGuard
Strict firewalls (e.g. China)
SSTP, OpenVPN (TCP)
Diagram: VPN Tunnel with OpenVPN
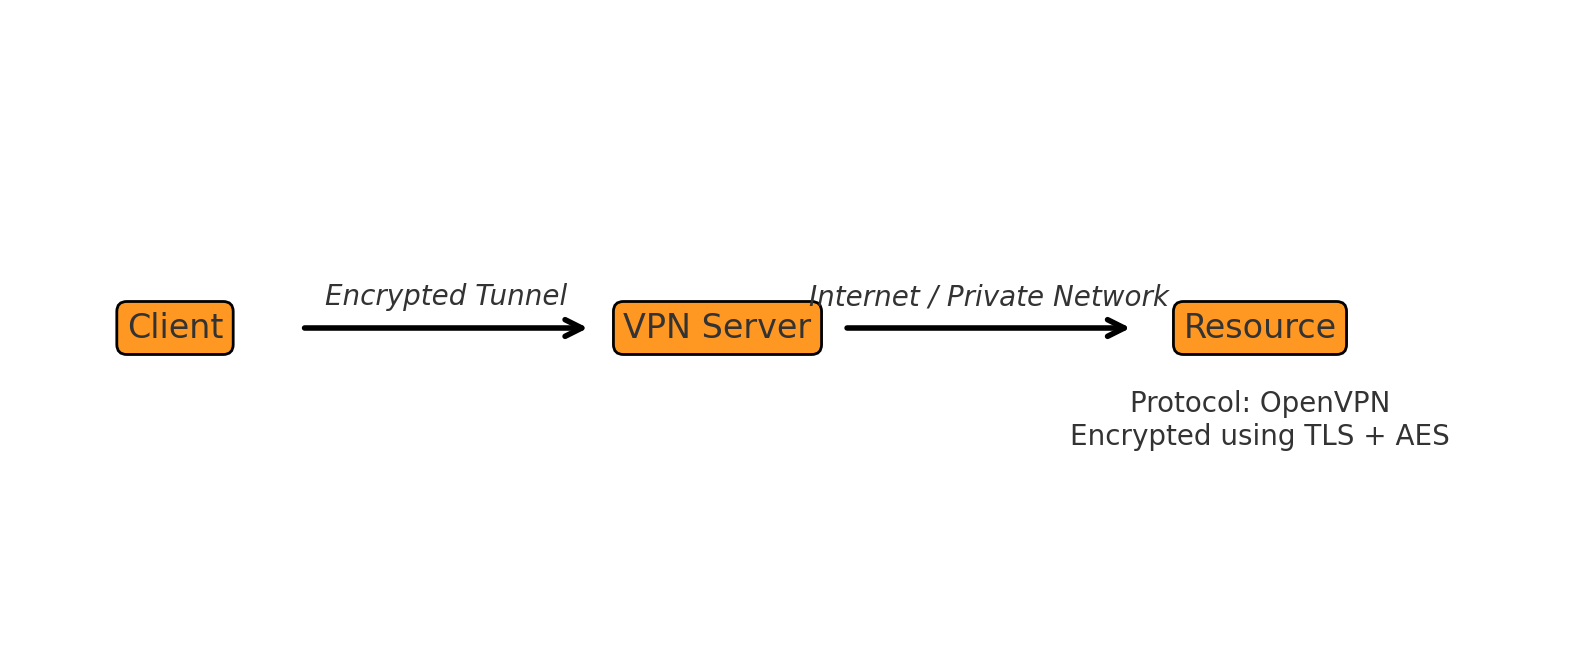
Packets are encrypted, tunneled, and forwarded using the selected VPN protocol
VPN Protocol Limitations
While VPNs are essential for security, they come with challenges:
- Manual configuration overhead: IP assignments, firewall rules, routes
- IP conflicts: Overlapping subnets across VPCs or users
- Performance bottlenecks: Single points of failure or latency hotspots
- Limited visibility: Hard to audit or monitor paths and policies
- Inconsistent NAT behavior: VPNs often fail when behind multiple NAT layers
- No service awareness: VPNs secure tunnels—not the services inside them
VPNs were designed for static workloads and trusted perimeters—not dynamic, multi-cloud microservices or IoT devices.
How noBGP Modernizes Private Connectivity
noBGP isn’t a VPN—but it solves the same core problems: secure, private connectivity between distributed systems.
Rather than building tunnels between networks or devices, noBGP creates dynamic, policy-based connections between workloads, without relying on traditional VPN protocols.
How noBGP Compares:
Feature
Traditional VPNs
noBGP
Protocol dependencies
OpenVPN, IPSec, etc.
None (custom encrypted overlay)
Needs static IPs/subnets
✅ Yes
❌ No
Handles CIDR collisions
❌ No
✅ Yes
End-to-end encryption
Optional/configurable
✅ Always-on
Cloud-native integration
❌ Limited
✅ Built for cloud, edge, K8s
Performance control
❌ BGP dependent
✅ Deterministic, policy-driven
NAT traversal
❌ Unreliable
✅ Seamless
When to Use noBGP Instead of a VPN
Use noBGP when:
- You need instant connectivity across clouds, without pre-planned IP ranges
- You want fine-grained control over what service can talk to what
- You’re tired of managing IPsec tunnels, key exchanges, and NAT rules
- You want encryption, routing, and identity in one layer
- You’re building modern apps with dynamic infrastructure
Final Thoughts
VPN protocols were a game-changer for secure remote access. But they were built in an era of fixed servers, trusted perimeters, and manual control.
Today’s applications are dynamic, distributed, and born in the cloud. They need programmable, identity-based networking—not hand-built tunnels.
noBGP goes beyond VPNs, offering a modern approach to secure, deterministic, and private connectivity. You don’t choose a protocol—you choose a path.
And with noBGP, it’s your path.
