Connect VPCs with Overlapping IP Ranges — Without NAT, Renaming, or Complex Routing
TL;DR: Connect Overlapping VPCs Without the Pain
- Subnet overlaps between VPCs are inevitable, default IP ranges like 172.31.0.0/16 cause conflicts across accounts, regions, and partners.
- Traditional fixes like NAT, CIDR renumbering, and proxies are disruptive, complex, and hard to scale.
- noBGP connects VPCs privately even with overlapping IPs, with no need for NAT, IP renaming, or complex routing.
- Setup is simple: deploy noBGP code in each VPC, no public IPs, no subnet translation, no infrastructure changes.
- Ideal for DevOps, cloud architects, and IT teams who need conflict-free, scalable multi-VPC networking.
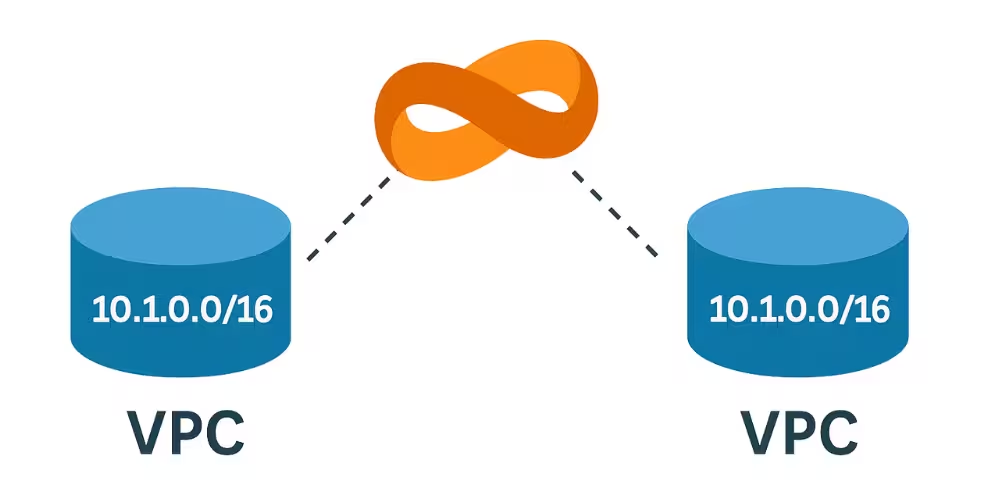
If you’re running multiple VPCs across AWS accounts, regions, or environments, subnet overlap and conflicting CIDR ranges are inevitable. Maybe your team used the default 172.31.0.0/16 CIDR block in staging and production. Or maybe a partner’s VPC has the same IP range as yours. Now what?
VPC peering fails. Connectivity breaks. Your options are limited.
You could:
- Try renumbering the CIDRs (disruptive and risky)
- Add NAT and proxy layers (complex and brittle)
- Build isolated workarounds (slow and hard to scale)
Or you can deploy noBGP.
✅ noBGP Solves Overlapping VPC Subnet Conflicts Instantly
noBGP creates private connections between overlapping VPC networks, even when CIDR blocks conflict — without requiring subnet changes or NAT workarounds. It just works.
- 🚫 No need to re-IP or rename VPC CIDRs
- 🔒 No NAT, VPN, or tunneling setup required
- 🔄 No impact to your existing infrastructure
🧠 No deep networking knowledge needed
🔧 How It Works
- Sign-up for a noBGP account
- Deploy code in each VPC
- Connect securely without public IPs or subnet translation
Whether it’s two VPCs or twenty, across accounts, clouds, or teams, noBGP lets you build connections without conflict.
👨💻 Who This Is For
This is for:
- DevOps teams managing multi-account AWS environments
- Cloud architects hitting CIDR collision limits
- Platform engineers who’ve run into VPC peering restrictions
- IT teams building staging, QA, or partner networks with overlapping IPs
🚀 Ready to eliminate VPC subnet overlap headaches?
Start building smarter, conflict-free VPC connectivity, without changing a single IP address.
👉 [Try noBGP free] or [Get a demo]
FAQ
❓ Can I peer two VPCs with the same IP range?
Not with AWS VPC peering, it will fail. But noBGP allows you to connect overlapping CIDRs without renaming or NAT.
❓ What’s the default AWS VPC IP range?
By default, AWS VPCs use 172.31.0.0/16, which often leads to CIDR block conflicts when multiple environments are created.
❓ Does this replace VPN or NAT gateways?
Yes. noBGP eliminates the need for NAT or VPNs when connecting private VPCs, no overlapping subnet issues.
